A new support representative arrives for the Monday shift. Their licence is active, but the inbox is missing, presence will not load, and the queue is still invisible. An administrator starts adding roles one by one. Six months later, nobody can explain why that person has more access than the rest of the team.
Microsoft Entra security groups offer a cleaner model for Dynamics 365 Contact Center. Put people in a group that reflects the work they do, connect that group to a Dataverse team, and assign the required roles to the team. The important part is not the shortcut. It is making membership the controlled source of access, with a test for both joining and leaving.
Start with work rather than names
Do not begin by copying the roles of the person sitting nearby. Define the job first. A frontline representative may need access to cases, presence, approved queues and conversation handling. A supervisor needs a different set of privileges. An administrator should not inherit frontline membership merely because they occasionally inspect a queue.
- 1Define the jobDescribe the approved work before selecting roles.
- 2Create the group pathLink one owned Entra group to one Dataverse team.
- 3Assign the approved rolesPut the base roles on the team and record direct exceptions.
- 4Test real workVerify sign-in, queue, presence and conversation handling.
- 5Prove removalRemove test membership and confirm that the former work is unavailable.
Microsoft says the group based feature became generally available on July 24, 2026. It links a Microsoft Entra security group to a Dataverse team and can give members roles such as Basic User, Customer Service Representative and Omnichannel agent. It also warns that people in several teams receive the combined privileges of those teams. That is convenient, but it is also where quiet overpermission begins. See the Microsoft feature announcement.
Write down one sentence for each group. For example, “Members handle retail support conversations in the main queue.” If the sentence contains two unrelated jobs, split the group. This is the same discipline behind useful role based workspace access and sensible security controls.
Build one group to team path
The path should be easy to draw on one page.
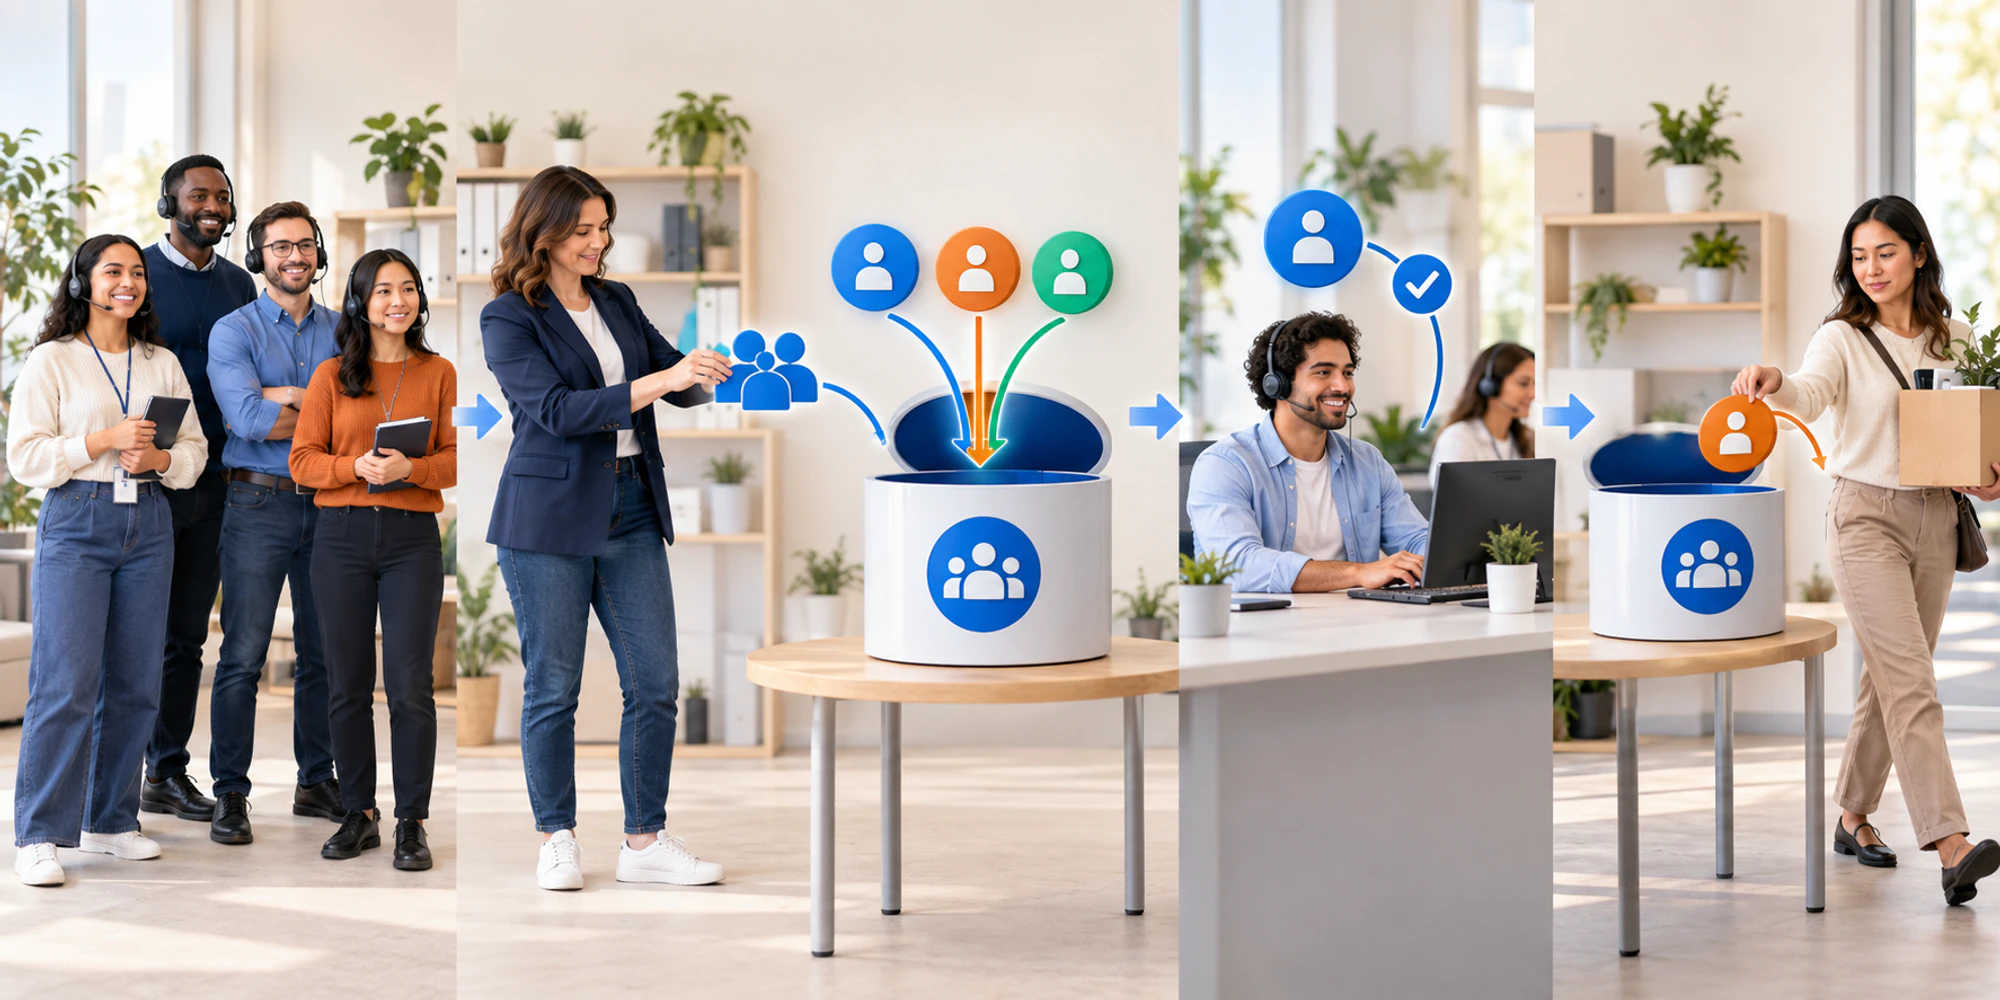
- A named owner manages membership in the Microsoft Entra security group.
- The group is linked to a Dataverse team of type Microsoft Entra ID Security Group.
- The team receives the approved Contact Center roles.
- A representative signs in and completes a real access check.
- Removal from the group triggers an equally serious loss of access check.
Microsoft's current role and user guide documents Basic User, Customer Service Representative and Omnichannel agent for a representative group. It also says direct role assignment remains necessary for role persona mapping. Group membership is therefore not an excuse to remove every direct assignment blindly. First identify which assignments are part of persona mapping, a custom application or a documented exception.
The operational owner and the platform administrator should agree on the boundary. The platform administrator controls the team and roles. The support owner decides who should do the work. Neither should silently do both.
Test access from the representative view
An administrator seeing a group in the portal is not proof that the job works. Use a licensed test account or a real new starter with a controlled checklist. Check the same path the representative will use during a busy shift.
| Evidence to capture | Passing result | Escalate when |
|---|---|---|
| Application sign in | The correct workspace opens | The user sees no app or the wrong app |
| Queue and presence | Approved queues and presence options appear | A required queue is missing or an unrelated queue appears |
| Conversation handling | The user can accept and complete permitted work | The user cannot act or can reach restricted work |
| Removal test | Access no longer permits the former job | Old queue or conversation access remains usable |
| Multiple group review | Combined access matches an approved job | Membership creates an undocumented privilege set |
Run the removal test before the design is called finished. Adding a user is the happy path. Offboarding, temporary cover and job changes expose the weak parts.
If access does not update as expected, do not solve it by adding another direct role. Compare the Entra membership, linked Dataverse team, team roles, licence and any direct assignments. Microsoft's guide notes that an optional synchronization action can be used when permissions must be synchronized immediately. Record whether you used it and retest.
Keep queue ownership separate from access
Group membership answers who may use a capability. It does not decide which conversation should go to whom today.
Your shared inbox assignment rules still need working hours, availability, language, account ownership and a monitored fallback. The team inbox needs one visible owner per conversation even when several people share permission to work it. A person can be allowed into a queue without being the right owner for every item in it.
This distinction prevents a common failure. An administrator adds someone to cover an absence, and the routing system immediately treats them as a permanent destination. Access may be correct while assignment is wrong. Test both, but approve them separately.
Make exceptions expire
Some people genuinely need more than the standard group. A supervisor may cover two regions. A migration lead may need temporary administration access. Give the exception an owner, a reason and an end date. Review it independently from the base group.
A monthly list of direct assignments is more useful than a huge screenshot of every member. Ask three questions. Does the person still do this job? Is the access supplied by the intended group? Does any second group create a privilege combination nobody approved?
DripTell uses the same practical idea in customer operations. Team permissions and conversation ownership should be explicit, while routing and customer context remain visible. If you want to map that operating boundary across your channels, you can talk to DripTell. The platform choice matters less than being able to explain why a person can see a customer conversation and how that access ends.
Frequently Asked Questions
Can Entra groups replace every direct Dynamics 365 role
No. Microsoft documents group based assignments for Contact Center users, but its role guide says role persona mapping still requires roles to be assigned directly. Preserve documented exceptions and test them instead of deleting them in bulk.
Which roles belong on a standard representative team
Microsoft's example uses Basic User, Customer Service Representative and Omnichannel agent. Your exact design still depends on the product configuration and the work the person is approved to perform.
How should we test offboarding
Remove the test user from the intended group, apply the documented synchronization path when timing requires it, then sign in as that user and verify the former workspace, queue and conversation actions are no longer available. Record the result rather than assuming the directory change completed every downstream step.
What should block the rollout
Stop if group ownership is unclear, a representative receives unrelated privileges, a required queue is missing, removal leaves usable access, or direct assignments cannot be explained. Those are access design failures, not onboarding inconveniences.
Want help applying this guide?Ask the DripTell team
From reading to action
Want help applying this to your business?
Share your details. We will read the article you are on and start with a useful answer for your team.
DripTell Editorial
Practical guidance reviewed by the DripTell product and customer workflow team.
See how DripTell checks product claims, uses primary sources and handles corrections.
Editorial and source policy