
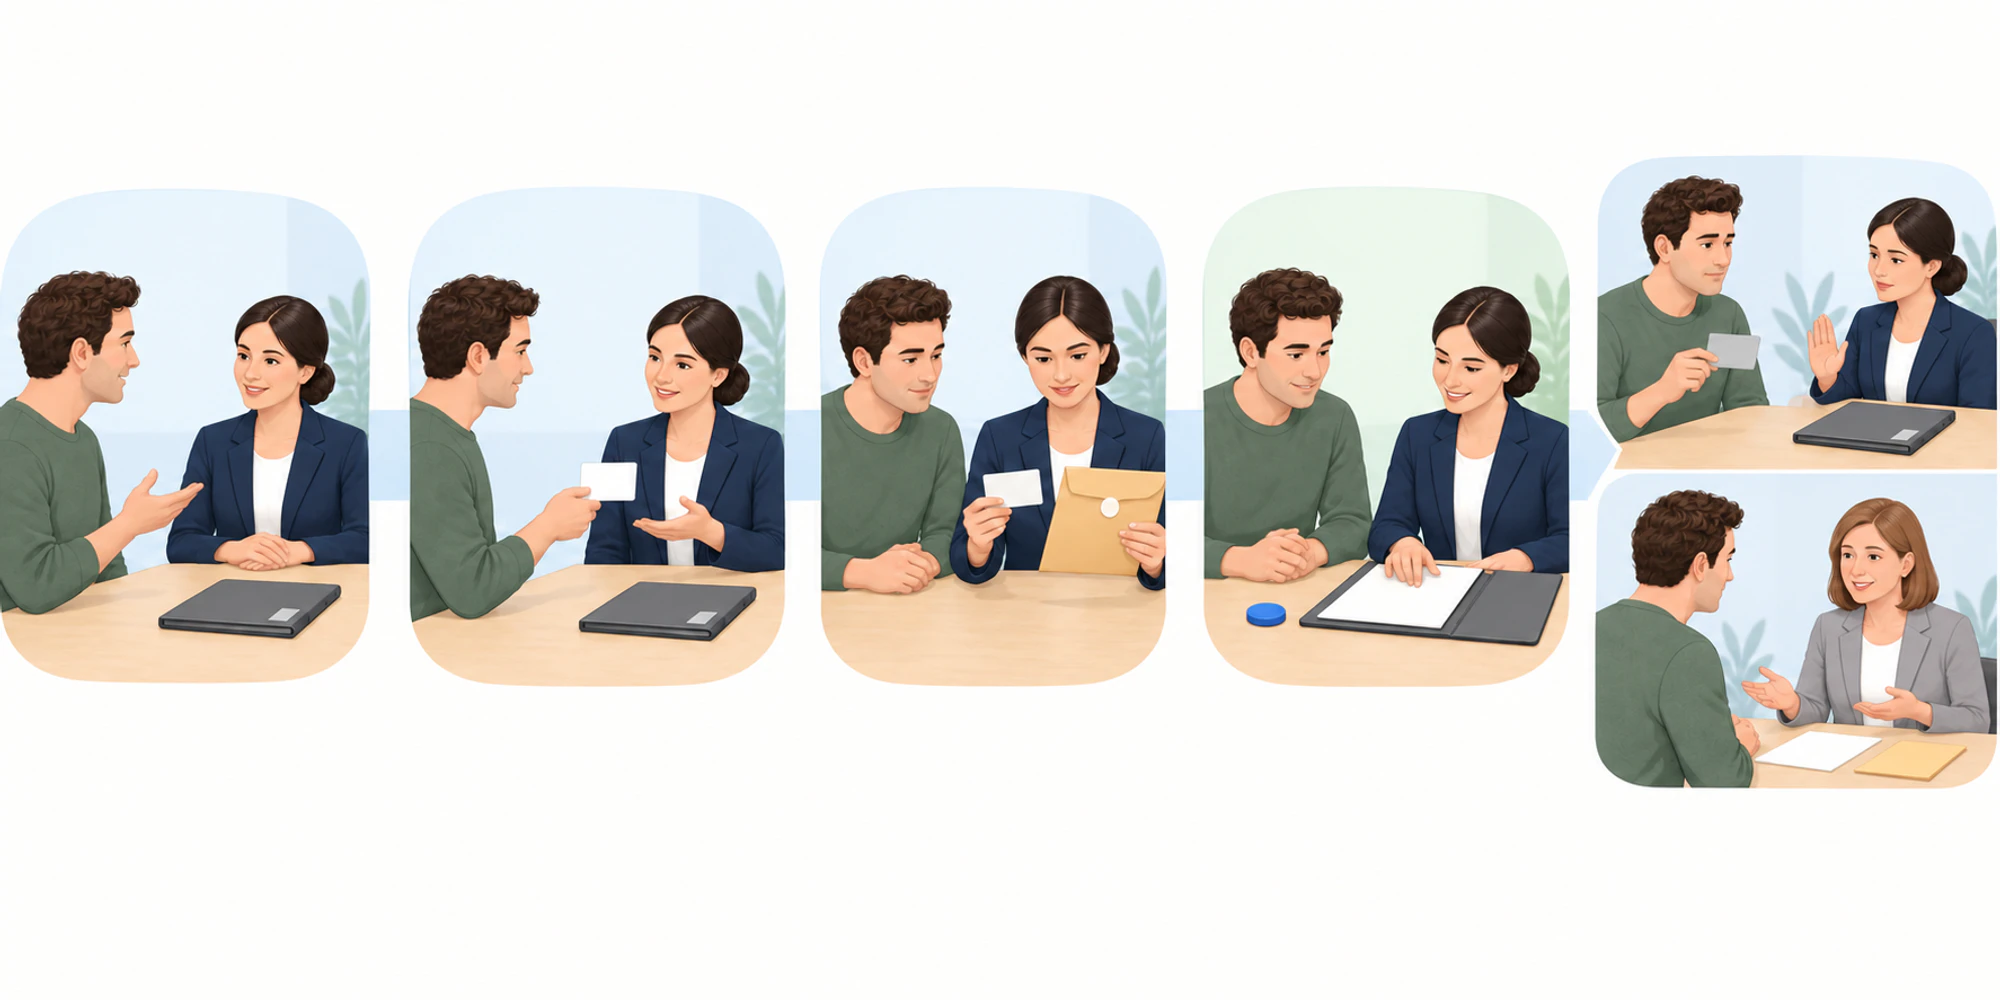
A customer starts a live chat by asking whether an order can be changed. That question is safe to answer anonymously. Five minutes later, the customer asks you to change the delivery address. The conversation has crossed a boundary. The team now needs reliable identity, but the customer should not have to start again.
That is the point of mid conversation authentication. The feature is not successful because a sign in window opens. It is successful when the right person becomes verified inside the same useful conversation, private work stays closed until then, and failure has a safe route.
Test the boundary before the button
Microsoft lists enhanced authentication for Dynamics 365 Contact Center as generally available in September 2026. The release adds OAuth 2.0 support alongside JWT based authentication, aligns authentication with Copilot Studio, and allows an anonymous customer in synchronous live chat to authenticate when a representative or AI agent prompts them. Microsoft also warns that release plan delivery can change, so confirm the capability in the intended tenant before planning a launch (Microsoft release details).
- 1Start safelyLet a customer ask a general question without proving identity.
- 2Prompt at the boundaryRequest authentication only before private account help begins.
- 3Link the right recordConfirm the intended active customer record and no other.
- 4Keep the conversationPreserve the transcript, owner and customer explanation after sign in.
- 5Recover without exposureKeep private data closed when authentication fails or expires.
Start by defining the authority boundary. A representative may explain opening hours or return policy without knowing who the visitor is. Viewing an order, changing an address, discussing an invoice, or exposing account history should wait for verified identity and whatever business authorization follows. Authentication proves identity. It does not automatically prove permission for every action.
Write two customer journeys before configuration
Most teams write only the successful journey. Write two. In the first, an anonymous customer authenticates and continues. In the second, the token is missing, expired, invalid, linked to the wrong active record, or delayed. The second journey prevents a rushed fallback from exposing private information.
| Situation | Expected identity state | What the team may do | Evidence to retain |
|---|---|---|---|
| General question | Anonymous | Give public guidance | Conversation starts without an account record |
| Private request | Authentication required | Explain why verification is needed | Prompt appears at the defined boundary |
| Valid identity | Authenticated | Continue within approved account permissions | Correct active customer record is linked |
| Invalid or expired token | Anonymous | Offer retry or safe manual help | Private fields remain unavailable |
| Ambiguous record | Unresolved | Escalate for controlled review | No record is guessed or merged |
Microsoft's configuration guidance says Dynamics 365 can distinguish anonymous from authenticated customers and can use defined context variables in rules. The representative sees an Authenticated value of Yes or No in the conversation summary. For a custom portal, Microsoft documents signed JWT claims, public key validation and a client function that should return the token within ten seconds. Invalid or expired tokens produce an error event (Microsoft authentication settings).
Keep the same conversation while authority changes
The customer should not repeat the original problem after signing in. Test that the transcript, current owner, queue history and the reason for contact remain intact. Then verify that the intended active contact or account is linked. A technically valid token attached to the wrong record is a failure.
This continuity matters in web chat, but it also matters after transfer. If the conversation enters a shared inbox, the next person should see the verified state and useful context without seeing a reusable token or unnecessary identity data. When an AI assistant asks the customer to authenticate, test that automation pauses when identity cannot be proven and that a person can take ownership cleanly.
Test failure before the happy path
Run expired, malformed and late token cases. Close the identity provider for one test. Sign in as a customer whose record is inactive. Open two browser tabs and confirm one customer's state cannot leak into another session. Let the token expire during a long conversation and observe what becomes unavailable.
Do not reward a failure with a weaker shortcut. The safe result is still useful. The representative can explain the next step, keep the public part of the conversation, offer a fresh authentication attempt, or move to a manual process whose controls are already approved. The representative must not guess the customer from a name, phone number or recent order description.
Separate identity routing and permission
Context variables can help route a verified customer, but test each decision separately. First ask whether the identity link is correct. Then ask whether the user may view or change the requested data. Finally ask whether the conversation should move to a different queue. One green result should not silently approve all three.
Review role based access for the people handling verified conversations. Confirm that security controls keep token material and unnecessary identity fields out of transcripts, exports and routine agent views. Also test the anonymous route. Authentication should not become a blanket barrier for a simple public question.
Decide what evidence permits launch
A launch record should show the tenant and channel tested, identity provider, test accounts, token lifetime, expected record match, allowed private actions, routing outcome, failure outcome and named owner. Capture results without storing live secrets or full tokens. Include at least one test completed by someone who did not configure the feature.
Set a stop rule. Pause rollout if the wrong record can be linked, a failed customer can see private data, the transcript is lost, ownership becomes unclear, or recovery depends on an improvised exception. Speed and branding can wait. Those failures cannot.
DripTell does not replace the identity provider or Dynamics authorization. Its useful role is downstream, where verified conversations need clear ownership, limited visibility and a safe handoff. If you are mapping that operating boundary across customer channels, the implementation team can help you define the evidence before adding more automation.
Frequently Asked Questions
Does mid conversation authentication replace authorization
No. It proves who the customer is. Your application and service policy still decide which records and actions that identity may access.
Should every live chat require authentication
No. Let people ask safe public questions anonymously. Prompt for authentication when the requested work reaches private account data or a protected action.
What is the most important failure test
Use a valid looking identity that maps to the wrong or inactive customer record. The system must not guess, merge, or expose data while the match is unresolved.
What should happen when authentication fails
Keep private information closed, preserve the safe part of the conversation, explain the retry or manual path, and leave the work with a named owner.
Want help applying this guide?Ask the DripTell team
From reading to action
Want help applying this to your business?
Share your details. We will read the article you are on and start with a useful answer for your team.
DripTell Editorial
Practical guidance reviewed by the DripTell product and customer workflow team.
See how DripTell checks product claims, uses primary sources and handles corrections.
Editorial and source policy

